

ID Document Authenticity
IDV Toolkit contains a set of features that can help detect some of the most common signs of suspicious onboarding attempts.
To provide trusted digital onboarding, it is important not only to verify the user using facial biometrics and liveness, but also to evaluate the authenticity of the identity document.
Capabilities of the Hardware
Due to the limitations of smartphone cameras, it is currently not possible to reliably detect all fake or forged documents like with a dedicated document scanner. The only reliable method to prove document authenticity with a smartphone is the NFC reading of e-documents with a RFID chip.
However, there are certain features within the IDV Toolkit that may help to detect some signs of suspicious onboarding attempts. Human supervision is recommended to review suspicious documents.
Document Authenticity and Photo Capture Method
It is important that during the onboarding process there is no possibility for the user to upload a photo him/herself. It has to be strictly enforced that the user takes a photo of the document using only the Document Auto Capture component. Being able to upload a photo of a document allows the user to make manipulations that cannot be detected.
Data Consistency
Biometric Validation
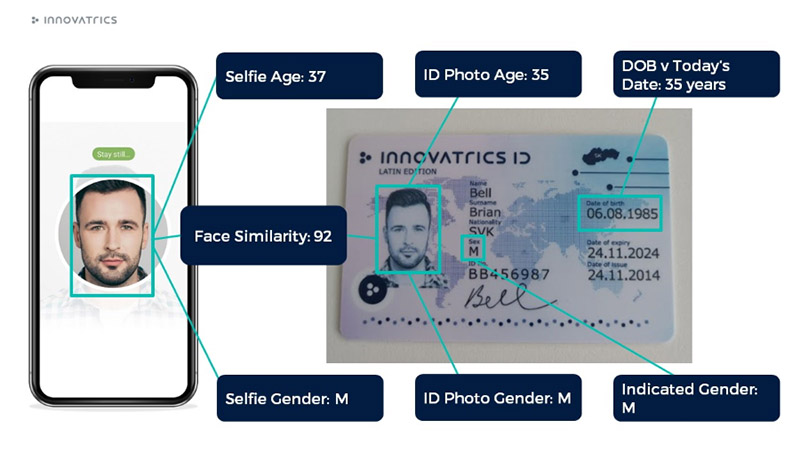
This is a core functionality of IDV Toolkit. Our face algorithm provides an estimate of age and gender for the person in the selfie photo, as well as for the face portrait on the document. This can be validated against the date of birth and gender on the identity document. The cross check of selfie vs document photo confirms that the same person provided the selfie.
This validation result can be obtained in the SelfieInspection object of the response of the customers/{id}/inspect API call, and in the PortraitInspection object of the reponse of the customers/{id}/document/inspect API call.
If there is a significant difference between these and expected values, this can trigger an alert during the process, and such cases may be rejected or passed to manual review, based on the workflow configuration.
Document Data Cross-check
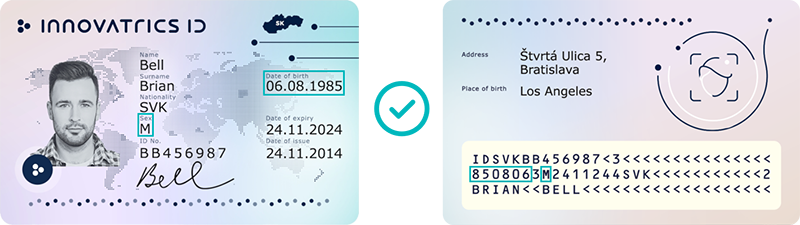
Some identity documents contain Machine Readable Zones (MRZ) and many have contactless RFID chips which can be accessed using NFC-capable smartphones. This provides two additional levels of document authenticity detection, as tampering with the MRZ field requires more advanced knowledge, and data from the RFID chip cannot be modified at all.
This validation result can be obtained in the VisualZoneInspection.TextConsistency object of the response of the customers/{id}/document/inspect API call.
RFID Chip Authentication
Besides the data cross-check, the document data read by NFC can be authenticated using Passive Authentication protocol. This is the only 100% reliable authentication method for ID documents. Read more in Passive Authentication
Visual Detection of Attacks
Older identity documents may not have RFID chips or an MRZ. IDV Toolkit can detect some simple methods of document forging, including black and white photocopies. It can also detect photos of documents taken from a monitor or laptop screen.
Screen and Print Attack Detection
The Digital Identity Service can detect, to a certain level, whether a photo of an ID document was taken from another screen, such as a laptop or monitor, or whether it shows a printed copy of the original document. Since Digital Identity Service 1.70.0 both are detected by one document liveness model. It returns one genuineness score per document page; when the score falls below the configured threshold, the page is an attack and the more probable of the two attack classes is reported. The result can be obtained in the response of the customers/{id}/document/inspect API call, per document page:
- PageTamperingInspection.looksLikeScreenshot is
truewhen the photo was taken from a screen. - PageTamperingInspection.looksLikePrintCopy is
truewhen the photo shows a printed copy. It isnullfor documents whose original is paper.
At most one of the two is true for a page. Both are returned whenever either check is enabled in the Digital Identity Service; in the default configuration only screen attack detection is enabled, and both flags are still populated.
For trust evaluation use the document_liveness trust factor (type SCORE, recommended reject threshold 0.86). It covers both screen and print attacks. The document_print_copy trust factor is deprecated since Digital Identity Service 1.70.0: it is still accepted in a request for backward compatibility, but it is ignored and produces no result.